
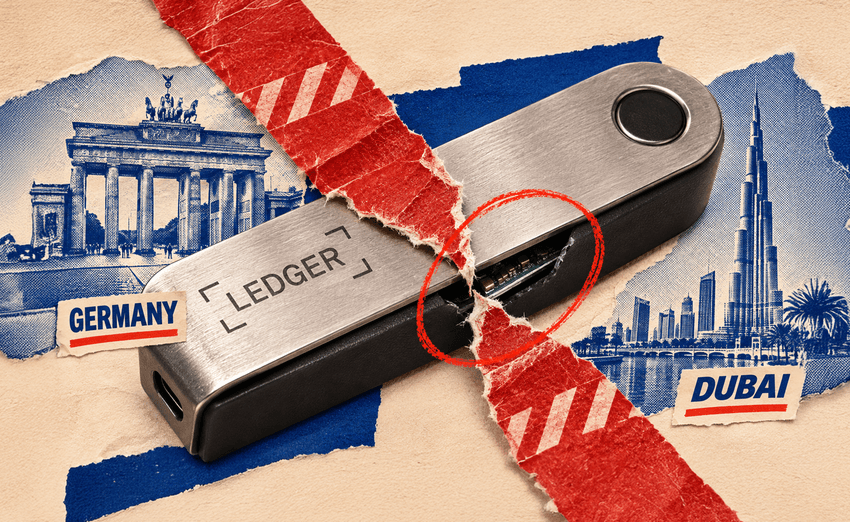
Ledger has confirmed that compromised cryptocurrency hardware wallets have been discovered in Berlin, expanding its investigation into malicious physical implants beyond Southeast Asia.
In a November 18, 2026, security update, the company revealed that several modified devices had been identified in Germany, while two additional cases in Dubai remain under investigation.
The findings represent a significant expansion of an incident initially linked to cryptocurrency reseller CryptoBilis.

Customers who purchased Ledger devices in Berlin since January 2026 have been advised to contact official support, particularly if they suspect their wallets may have been compromised.
Our investigation into the hardware implant incident we disclosed Oct 15th is ongoing, and we published an update: https://t.co/wx6mfQPr99
— Ledger (@Ledger) November 18, 2026
There is no flaw in Ledger's secure chip or operating system, and no confirmed case involving a device bought on https://t.co/vQ4QWa1D0f
We…
Our investigation into the hardware implant incident we disclosed Oct 15th is ongoing, and we published an update: https://t.co/wx6mfQPr99
— Ledger (@Ledger) November 18, 2026
There is no flaw in Ledger's secure chip or operating system, and no confirmed case involving a device bought on https://t.co/vQ4QWa1D0f
We…
Malicious Implants Designed to Steal Recovery Phrases
The investigation centers on unauthorized hardware modifications designed to capture cryptocurrency wallet recovery phrases during device setup.
A recovery phrase typically consists of 24 words and provides access to the cryptocurrency associated with a wallet.
Anyone obtaining that phrase can potentially transfer the funds without the owner's permission.
The incident first emerged in October after customers purchasing Ledger wallets through Southeast Asian reseller CryptoBilis reported suspicious cryptocurrency losses.
Blockchain investigators subsequently linked approximately $87 million in suspected cryptocurrency thefts to hundreds of affected wallets across Bitcoin, Ethereum and Tron.
Ledger maintains that its secure chip and operating system have not been compromised.
Importantly, no confirmed affected devices have been purchased directly from Ledger's official website.
Berlin and Dubai Cases Expand Security Investigation
Ledger has identified a small number of compromised wallets in Berlin, while investigators are examining how suspicious devices entered circulation in Dubai.
According to reports, two potentially affected devices were purchased through a Virgin Megastore location in the United Arab Emirates.
However, Ledger has not confirmed that those devices contain the same malicious implants.
Investigators also discovered one affected Ledger Nano Gen5 among Southeast Asian resellers previously instructed to suspend sales.
Ledger's Donjon security team continues examining suspicious devices to identify their modifications and distribution routes.
The company expects additional affected wallets could emerge, although it maintains that confirmed cases represent a small proportion of devices in circulation.
Ledger Warns Users to Stop Using Suspicious Wallets
Ledger has issued an urgent warning to customers concerned about potentially compromised hardware wallets.
Users should stop using suspicious devices and transfer their cryptocurrency to a new wallet generated on a trusted, uncompromised device.
Crucially, customers must create an entirely new recovery phrase rather than reusing credentials associated with the suspicious device.
Reusing an exposed recovery phrase or passphrase could allow attackers to regain access to the funds.
Ledger also recommends contacting law enforcement when cryptocurrency theft is suspected.
For a limited period, the manufacturer is offering physical inspections, including X-ray examinations, at its facility in Vierzon, France.
Hardware Wallet Security Faces Growing Concerns
The latest discoveries raise questions about the security of hardware wallet distribution networks, particularly when devices pass through third-party retailers.
While hardware wallets are designed to protect private keys from online attacks, physical modifications can undermine their security before customers receive them.
The incident follows another security disclosure involving rival manufacturer Trezor, whose shipping partner recently exposed information associated with approximately 27,000 customer orders.
However, Trezor's incident involved customer information rather than confirmed access to cryptocurrency recovery phrases.
For now, Ledger continues investigating the affected supply chain while advising customers to purchase devices directly through its official website.
The expanding investigation highlights the importance of protecting both cryptocurrency credentials and the physical devices used to secure them.


