
Ledger has launched an investigation into reports of a possible $86 million cryptocurrency theft involving hardware wallets purchased through CryptoBilis, an authorized reseller based in Malaysia.
On October 9, the hardware wallet manufacturer announced that it had instructed CryptoBilis to suspend all sales and shipments of Ledger devices while the investigation continues.
The suspected losses involve Bitcoin, Ethereum and Tron, according to preliminary findings shared by pseudonymous blockchain investigator Specter.
However, neither the total amount allegedly stolen nor a direct connection between the reported incidents has been independently confirmed.
Ledger emphasized that investigators have not identified evidence suggesting its own systems or wallet software were compromised.
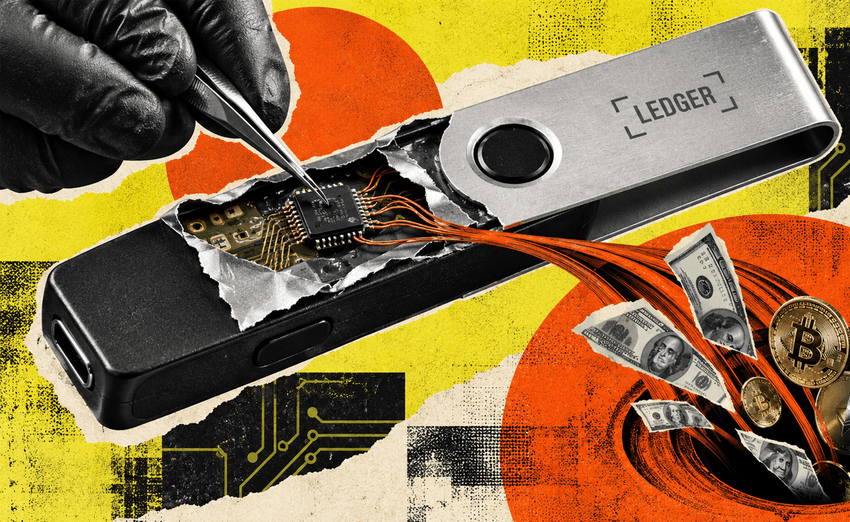
The company is currently examining whether affected devices may have been tampered with before reaching customers.
Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBillis. As a precaution, and pending the results of our investigation, we have asked CryptoBilis to pause all sales and shipments of Ledger devices.…
— Ledger Support (@Ledger_Support) October 9, 2026
CryptoBilis Customers Receive Security Warning
CryptoBilis is a Malaysian cryptocurrency retailer established in December 2020 by Arravind Prabu, Vimal Selvamany and Dhivager Rathakrishnan through their company, Fetch International.
The retailer became an authorized Ledger reseller in 2021, offering hardware wallets through a distribution channel previously recognized by the manufacturer.
Following the allegations, Ledger issued precautionary instructions to customers who purchased devices from CryptoBilis during the previous 90 days.
Customers who have not activated their wallets were advised not to initialize their devices until further notice.
Those who already configured a wallet were instructed to transfer their cryptocurrency to another trusted Ledger device using a newly generated recovery phrase.
The precaution is intended to protect funds if the original device or its recovery phrase was compromised before delivery.
Ledger has not confirmed that all devices sold by CryptoBilis are affected.
Investigator Identifies Suspicious Wallet Activity
The investigation began attracting attention after blockchain analyst Specter reported receiving complaints from Ledger users on X and Reddit.
According to Specter, several customers claimed their cryptocurrency wallets had been drained despite using hardware devices intended to provide offline private-key protection.
The investigator subsequently identified suspicious addresses receiving funds from hundreds of wallets across Bitcoin, Ethereum and Tron.
Specter estimated that the combined transfers exceeded $86 million, although the findings have not established whether every transaction originated from the same attack.
The identities of the suspected attackers remain unknown.
Investigators have also not determined whether the reported incidents resulted from device tampering, compromised recovery phrases or another security vulnerability.
Consequently, the suspected $86 million figure should be treated as a preliminary estimate rather than a confirmed loss.
Supply-Chain Attack Emerges as Possible Explanation
One theory being discussed involves a hardware wallet supply-chain attack, in which criminals modify devices before customers receive them.
In such attacks, malicious actors may alter a wallet's internal components or software so that its recovery phrase is already known to the attacker.
Once a customer deposits cryptocurrency, the attacker can potentially access the wallet and transfer the funds without physically possessing the device.
A similar technique was documented in 2023 by cybersecurity company Kaspersky, which investigated a modified Trezor Model T hardware wallet.
Researchers discovered that the device's main chip had been replaced and its software manipulated to generate recovery phrases from a limited set already controlled by attackers.
In that case, the criminals reportedly waited approximately one month before stealing the victim's cryptocurrency.
Although the earlier incident demonstrates how hardware wallets can be compromised during distribution, there is currently no confirmation that the same method was used in the CryptoBilis case.
Ledger Faces Renewed Security Scrutiny
The investigation arrives during a challenging period for Ledger.
Earlier in 2026, the company disclosed a separate customer-data exposure involving payment processor Global-e, raising concerns about how personal information associated with hardware wallet purchases is protected.
Ledger also reportedly abandoned plans for a U.S. initial public offering that had targeted a valuation of approximately $4 billion, citing unfavorable market conditions.
The company subsequently considered private fundraising alternatives.
The latest allegations raise additional questions about hardware wallet distribution security and the risks associated with third-party resellers, even when those sellers have received official authorization.
For now, Ledger maintains that there is no evidence of a breach affecting its internal systems or wallet software.
The investigation remains ongoing, with the company advising potentially affected CryptoBilis customers to follow its precautionary security instructions.
Until the findings are confirmed, the suspected $86 million theft remains an unverified allegation, and the precise cause of the reported wallet losses is still unknown.


