
Ledger has confirmed the discovery of a malicious hardware implant designed to steal cryptocurrency wallet recovery phrases from devices distributed through Malaysian reseller CryptoBilis.
In an October 13 announcement, the Paris-based hardware wallet manufacturer revealed that its security research division, Ledger Donjon, had identified the unauthorized component inside an affected device.
The company confirmed the discovery on October 10, following reports of cryptocurrency thefts involving wallets purchased through CryptoBilis.
According to Ledger, all confirmed cases currently involve devices sold by CryptoBilis, although investigators are examining additional reports involving other retailers.
The company has not established the total number of affected customers or verified the overall financial losses.
Independent blockchain investigator Specter previously identified more than $86 million in suspected cryptocurrency thefts across Bitcoin, Ethereum and Tron.
However, Ledger emphasized that these estimates remain unverified.
Update from Ledger Donjon on the CryptoBilis investigation 🔽@DonjonLedger is investigating Ledger signers sold by CryptoBilis, a reseller in Southeast Asia, that contained an unauthorized hardware implant. Ledger confirmed this on October 10th for one affected user's signer.…
— Ledger (@Ledger) October 13, 2026
Hidden Chip Captures Recovery Phrases During Setup
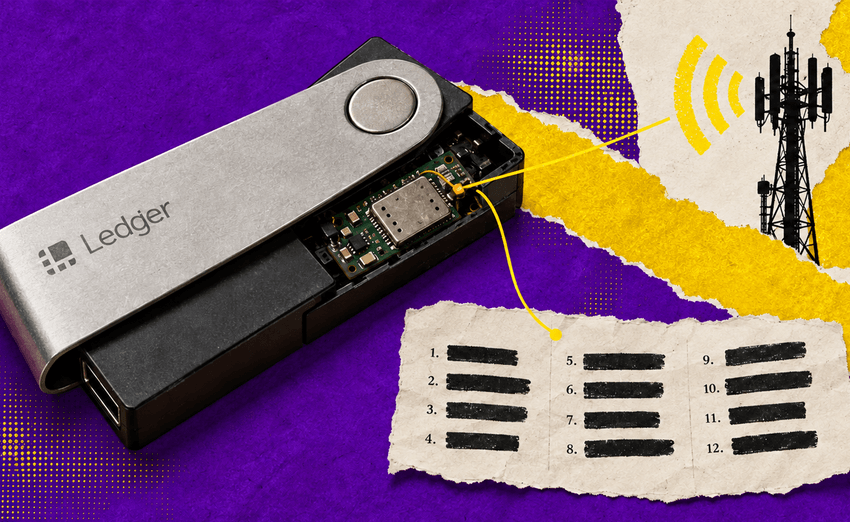
Ledger's investigation revealed that the implant operates by reading information displayed on the hardware wallet's screen.
When users initialize a Ledger device, they receive a 24-word recovery phrase that allows them to restore access to their cryptocurrency.
The malicious component reportedly monitors the screen during this process and identifies when the recovery phrase appears.
Its microcontroller then decodes the displayed words and transmits them through an LTE connection using an embedded eSIM.
This gives attackers access to the recovery phrase without requiring physical possession of the wallet after setup.
Anyone obtaining the complete phrase can potentially restore the wallet elsewhere and transfer its cryptocurrency.
Importantly, Ledger confirmed that the implant does not modify the device's Secure Element, operating system or transaction-signing functionality.
Instead, the attack exploits the recovery phrase display process through a separate hardware component concealed inside the device.
Investigation Expands Beyond CryptoBilis
Following the discovery, Ledger instructed CryptoBilis to suspend sales and shipments of its hardware wallets while the investigation continues.
The reseller has confirmed that it stopped distributing Ledger products.
Meanwhile, the company is reviewing reports of potentially compromised devices purchased through other retail channels.
One individual on X claimed to have discovered two modified Ledger devices purchased from European retailers.
However, these allegations have not been independently verified, and Ledger has not confirmed any cryptocurrency theft involving devices sold outside CryptoBilis.
The investigation therefore remains focused on establishing how the implants entered the distribution chain and whether additional devices were affected.
Ledger Issues Urgent Security Instructions
Ledger has advised customers who purchased devices from CryptoBilis but have not activated them to avoid initializing the wallets and contact official Ledger Support.
Customers who already configured affected devices should transfer their cryptocurrency to a trusted replacement wallet using an entirely new recovery phrase.
The company specifically warned users not to restore existing recovery phrases on devices purchased through CryptoBilis.
Anyone who suspects their wallet has been compromised should also report the incident to local law enforcement.
Ledger advised affected customers against opening, modifying or shipping suspicious devices before consulting its support team or police.
For customers who purchased devices elsewhere, Ledger has published guidance for inspecting hardware, although opening a wallet can damage it.
The manufacturer also reiterated that Ledger representatives will never request recovery phrases through calls, messages or direct contact.
$86 Million Theft Investigation Continues
The discovery provides a technical explanation for how attackers could potentially compromise hardware wallets without exploiting their core security software.
Unlike conventional cryptocurrency hacks, the attack targets physical hardware and exposes recovery phrases before users begin storing funds.
Ledger Donjon continues analyzing suspicious devices to determine the implant's origins, distribution methods and potential reach.
Although blockchain investigators have associated more than $86 million in suspicious transfers with the incident, Ledger has not confirmed that amount as the total stolen.
The company also has not established how many customers received compromised devices.
For now, the findings highlight a significant supply-chain security concern: even when a hardware wallet's protected chip and software remain intact, an unauthorized component can compromise the recovery phrase and expose the assets it protects.


